Cybersecurity depends on technical controls and human decisions
Security products can be present while a control has quietly stopped working — an account was never deprovisioned when someone left, a vendor holds more access than the contract allows, or the incident response plan names two people who no longer work there.
The Verizon Data Breach Investigations Report (DBIR) documents multiple routes into organizations, including vulnerability exploitation, credential abuse and social engineering. These findings support testing technical controls alongside the decisions people make when granting access, responding to requests and handling sensitive information.
Questions you might have
How Falcone International helps with addressing your strategic needs
The consequences of a breach can extend beyond immediate remediation. Depending on the applicable law, risk and contracts, it can trigger regulatory notification, client disclosure and an internal review. It can also affect later due diligence. The work below is aimed at the gap between the security program on paper and the one that actually operates.
We help clients find the vulnerabilities in their systems, design and implement the measures that close them, and monitor what is running afterward — and, where something has already happened, work the incident itself.
- Cybersecurity Perspectives: Provide advice and recommendations on improving clients' cybersecurity posture, including risk assessments, policy and procedure development, and compliance audits.
- Threat Intelligence: Identify potential threats and vulnerabilities and provide recommendations on mitigating those risks.
- Network Security: Design and implement security measures to protect an organization's networks from unauthorized access, including firewalls, intrusion detection/prevention systems, and network segmentation.
- Vulnerability Assessments and Penetration Testing: Identify vulnerabilities in an organization's systems and applications and test them to determine their level of resilience against attacks.
- Incident Management: Respond to cybersecurity incidents, including investigating, containing, and recovering from security breaches and attacks.
- Security Operations Center (SOC) Advisory: Assess, or help establish, 24/7 monitoring and management of an organization's security infrastructure, including threat detection and response, incident management, and threat hunting.
- Security Awareness Training: Educate employees on how to recognize and respond to security threats and promote a culture of security within an organization.
-
Compliance and Regulatory Services: Ensure an organization's compliance with relevant industry regulations and standards, such as HIPAA, PCI-DSS, and GDPR.
Staff, vendors and contractors can create security risks through compromised accounts, mistakes or malicious actions. Technical controls should limit and monitor legitimate access, while training and vendor reviews address how people use it.
If you already have a mature program
Some clients do not need a security program built. They need someone independent to test the one they already have, without the engagement turning into an argument with the team that built it. We work alongside an existing function rather than over the top of it.
In practice that means audits aimed at the subtle gaps rather than the obvious ones, threat intelligence scoped to your actual sector and footprint instead of a general feed, and penetration testing or red team exercises that pursue a defined objective the way an attacker would — rather than a scan with a report attached to it.
It also means compliance work that tracks regulatory change before it becomes a finding, and training built around the decisions your people actually face rather than a generic awareness module. The test of any of it is simple: when the engagement ends, can you name what changed?
Prevention asks whether you can keep an attacker out. Resilience asks what happens on the day one gets in: whether the business keeps running, how quickly you can establish what was reached, and how long it takes to operate normally again. Planning must address both questions.
Where programs usually have gaps
Well-run programs still have blind spots, and they tend to sit in the same few places. Our audits are scoped to look there first.
Common gaps in programs
The most common is an incident response plan nobody has rehearsed — a document that assigns roles rather than a process anyone has run under pressure. The second is insider risk, deliberate and accidental, which is usually a consequence of access granted for a project and never withdrawn. The third is new technology and third-party integrations, which arrive between assessment cycles and are rarely scoped back into them.
What the audit covers
The audit deliberately reaches past the security team’s own perimeter, because that is where unowned risk collects. It covers data governance and privacy policy measured against current regulation; supply chain security, since your exposure now includes your suppliers’ exposure; and physical security where it meets the digital — badge systems, building access, how hardware is issued and returned.
It also covers the policies themselves: not whether they exist, but whether the people bound by them behave as though they do. Social engineering succeeds against organizations with excellent written policy all the time, which is why we treat training as part of the control set rather than an adjunct to it.
Cloud and remote infrastructure
Cloud services and remote work moved a large share of most organizations’ infrastructure outside the boundary the security program was originally drawn around. We scope audits to cover it as it actually runs, including the parts procured by individual teams without going through IT — which is usually where the surprises are.
The output is a ranked list of what to fix, what each item will take, and what can safely wait. Not a score.
Where to start
If you are not certain whether your program carries the gaps described above, that uncertainty is itself the finding worth acting on. It is also the cheapest question on this page to answer.
We can run the assessment, build and implement what is missing, or take on the operational monitoring — and if something is already underway, we can work the incident. The first conversation costs nothing and usually establishes which of those you actually need.
How the engagement runs
Whether we are assessing a mature program or building one, the sequence is the same.
Scoping regularly turns up the finding that matters most: infrastructure procured by individual teams without going through IT, which sits outside the boundary the security program was drawn around.
Straight answers
What are our most significant threats?
The priorities depend on your organization. Common exposures include unpatched externally facing services, compromised credentials and third-party access. Verizon’s 2026 DBIR identifies vulnerability exploitation as the leading initial breach vector in its dataset.
How effective are our current measures, and what should we measure?
Useful metrics are behavioral rather than tooling counts: time to detect, time to revoke access when someone leaves, percentage of third parties with a current access review. Number of blocked attacks tells you almost nothing.
Is our incident response plan effective?
Only testable by running it. The common failures are a contact list that has aged, no named decision-maker out of hours, and no agreed threshold for involving counsel.
How do we handle third-party risk?
Start with an accurate list of who has access to what, which most organizations cannot produce on request. Where a supplier relationship is material, this becomes a due diligence question rather than a technical one.
Are we compliant with GDPR, HIPAA, PCI-DSS?
Compliance and security overlap without being the same thing; it is entirely possible to be compliant and exposed. We assess both and are explicit about which finding is which. The human layer is addressed through workshops and training.
Get in touch about Cybersecurity
Let us talk about your Cybersecurity needs. We are here to help and are happy to give a non-binding and confidential assessment of your case and course of action. Contact Falcone International today for expert assistance.
Further reading
Selected from our Book of the Month series for their bearing on this service.
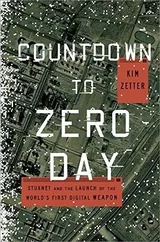 Countdown to Zero Day
Zetter’s reconstruction of Stuxnet established, definitively, that industrial control systems are targets and that code can break machinery. If you are assessing exposure beyond the corporate network, this is the case study everything else gets measured against.
 Glass Houses
Brenner argues that our exposure is structural — a consequence of how connected systems were built — rather than a failure of any particular control. It is the book that reframes cybersecurity from a procurement question into a design and governance one.
 People Hacker
Radcliffe talks her way into buildings for a living, and describes plainly how much of that work is done with material the target published itself. It is the sharpest account available of the human layer, which is the part of the attack surface almost nobody tests.