Engaging workshops and training sessions for teams ranging from general management to specialists
We run workshops and training for management teams and specialist groups, from single sessions to multi-day programs. Each one is built around the decisions your people actually have to make, which we establish before writing anything.
Topics we frequently cover in workshops and training sessions
Why invest in workshops and training sessions?
Participating in our training programs provides a variety of benefits for your organization, such as enhancing your security measures, mitigating risks, and ensuring the safety of your employees, executives, and operations. By investing in our training programs, you can be confident that you're taking the necessary steps to protect your organization and its assets from potential threats.
Our experienced trainers and instructors are dedicated to providing you with the most up-to-date information and skills needed to help you stay ahead of any potential risks or threats. Whether you're looking to enhance your security protocols, learn how to respond to emergencies, or develop a better understanding of threat assessments and risk management, Falcone International is here to help.
Most security failures involve a person making a reasonable-looking decision under pressure, not a technical breach. Training works when it rehearses the specific approaches an organization is likely to meet, so the judgment is already formed before the moment it is needed.
Benefits of conducting workshops or training sessions across your organization and teams
Risk reduction - By educating employees about potential security threats and fraud schemes, companies can reduce the likelihood of a security breach or fraud occurring.
Compliance - Many industries have regulations and compliance requirements that mandate certain types of security and anti-fraud measures, such as HIPAA for healthcare or PCI-DSS for payment card processing.
Reputation - Security breaches and fraud can damage a company's reputation and lead to loss of customer trust and loyalty.
Financial Loss - Security breaches and fraud can result in significant financial losses for a company, including the cost of recovering from the incident and any legal or regulatory fines.
Staff who know what to report - Training gives people the ability to recognize suspicious activity and, just as importantly, a route to report it that they trust enough to use.
A detailed look at the topics that can be covered
- Information security: best practices for protecting sensitive data and systems from unauthorized access, use, disclosure, disruption, modification, or destruction; including topics such as risk management, access control, encryption, network security, incident response, and disaster recovery; how to implement security policies and procedures; how to secure and manage mobile devices, how to identify and report security incidents and how to comply with relevant laws and regulations; how to recognize and avoid common threats, such as phishing and social engineering, and on how to handle sensitive information securely.
- Cybersecurity: techniques for securing a company's network, including intrusion detection and prevention, the use of virtual private networks (VPNs), best practices for securing mobile devices, such as smartphones and tablets, how to protect against mobile malware, how to respond to a security incident, such as a data breach, and how to minimize the damage and recover as quickly as possible.
- Phishing and social engineering: how to identify and prevent phishing scams, and how to avoid falling for social engineering tactics, different methods and techniques used by attackers to trick individuals into disclosing sensitive information or performing unwanted actions, how to identify and avoid phishing emails, text messages, and phone calls, as well as how to spot and avoid social engineering tactics in person or online, best practices for reporting suspicious activity and steps to take if an employee falls for a phishing or social engineering attack.
- Fraud detection and prevention: how to identify different types of fraud that can occur within an organization, such as financial fraud, identity theft, and skimming, identify and report suspicious activities and transactions, as well as best practices for preventing fraud, such as creating and implementing internal controls, monitoring for unusual activity, and conducting regular audits, how to respond to fraud incidents, including how to conduct investigations, and how to minimize the damage and recover as quickly as possible.
- Counter-intelligence: how to protect a company from espionage and sabotage by competitors, hostile governments, or other adversaries, learn about the various methods and techniques that adversaries may use to gain access to a company's sensitive information and resources, information on how to identify and prevent espionage, sabotage, and other malicious activities, best practices for maintaining operational security and protecting sensitive information, such as creating security protocols and procedures, implementing physical security measures, and training employees on how to identify and report suspicious activity.
- Insider threat: how to identify and prevent threats from within the company, such as embezzlement, sabotage or leaking of sensitive information.
- Business continuity: master the steps and procedures that a company should take to minimize the impact of a disruptive event, such as a natural disaster, cyber-attack, or pandemic, how to create a business continuity plan, assessing and identifying risks, developing strategies for disaster recovery and incident response, and testing and training on the plan to ensure it is effective, ensure the plan's relevance in light of changing circumstances and potential new risks.
- Compliance: how to comply with laws, regulations, and standards that apply to a company's industry or specific business operations (such as HIPAA, PCI-DSS and GDPR), overview of the key requirements and the potential consequences of non-compliance, best practices for achieving and maintaining compliance, how to identify and manage compliance risks, how to respond to and report compliance breaches, how to implement compliance policies, procedures and controls and how to conduct internal audits to ensure compliance.
How a program is built
Sessions are built around the decisions your people actually face, which we establish before writing anything.
The discovery stage is what separates training from a presentation. A session built on a generic deck teaches the topic; one built on the decisions your staff actually face changes what they do.
Straight answers
How long are sessions?
From a half-day briefing to multi-day programs. Length follows the objective: awareness needs hours, changing a procedure needs practice and a follow-up.
Who should attend?
Usually a wider group than expected. The people who first notice fraud, phishing or a safety problem are rarely the ones on the invitation list, and the finance and administrative staff who handle payment instructions are frequently the highest-value audience.
Does training actually reduce incidents?
It reduces some and not others. It works on recognition — noticing a pretext, spotting an irregular instruction. It does not fix a control gap, and it should not be sold as though it does.
Can you use our own cases?
Yes, and it is markedly more effective. An anonymized incident from your own organization holds a room in a way a generic example never does.
What is the most common mistake?
Running awareness training while leaving the reporting route slow or unsafe. If people who raise something are treated as an inconvenience, training teaches them to recognize problems they will then decline to report.
Talk to us about what workshop or training sessions you need
We are ready to help you with the above challenges. Contact us today to learn more about how our training programs can benefit your organization and help you stay ahead of potential security risks.
EVENT Spotlight
Tobias Jaeger, Founder of Falcone International, teaches this three-day program at the Amsterdam Institute of Finance, covering operational risk, resilience and crisis management. The falling dominoes are the course’s own image: the subject is where a chain of consequences can still be interrupted.
Mastering Operational Risk, Resilience, and Crisis Management
Our Founder, Tobias Jaeger, teaches this three-day hands-on Mastering Operational Risk, Resilience, and Crisis Management program at AIF — Amsterdam Institute of Finance. The course covers operational risk management for finance professionals across strategic, financial, operational and reputational risk, and how organizations absorb shocks rather than merely anticipate them. It also covers crisis management, for the cases where the risk management did not hold.
Further reading
Selected from our Book of the Month series for their bearing on this service.
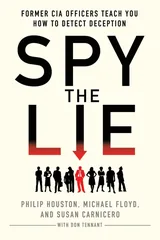 Spy the Lie
The method here transfers into interview training more directly than almost anything else in the literature, because it was written to be taught. It gives participants something to practice rather than something to agree with.
 People Hacker
Barratt is clear about why awareness training fails when it simply tells staff to be suspicious of everybody. Her alternative — specific, permission-giving verification behaviors — is what effective training actually installs.
 How Spies Think
Omand’s framework is teachable in a way most decision-making advice is not, because it breaks judgment into four separable questions. It works well as the spine of a structured-thinking session.