An accounting discrepancy of seventy-five cents.
That is where it started. An astronomer working as a systems administrator at Berkeley in 1986 was asked to resolve a trivial imbalance in the computer usage accounts. Rather than writing it off, he traced it — and found an intruder inside the network who had come from West Germany and was selling what he found to the KGB, conduct for which a West German court convicted him of espionage in 1990.
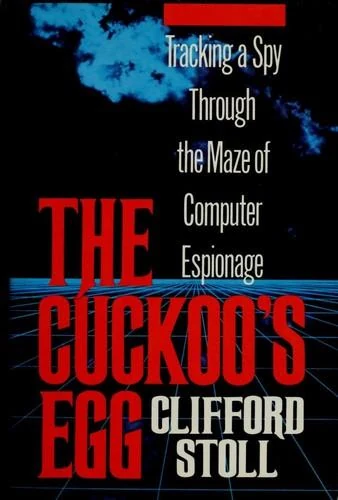
The Cuckoo's Egg is Clifford Stoll's account of that pursuit. It is the founding text of intrusion investigation, and it is still the best argument in print for not ignoring the small anomaly.
Summary
In The Cuckoo’s Egg, Clifford Stoll recounts the intrusion investigation he ran in 1986 as an astronomer handling systems administration at Lawrence Berkeley National Laboratory. A seventy-five-cent discrepancy in the computer usage accounts led him to an intruder from West Germany who was selling material to the KGB. Stoll monitored the intruder without alerting him and kept a logbook of every session. He worked out how the intruder moved between systems and built a honeypot of fabricated documents to hold him online for a trace. His attempts to interest the FBI, CIA, NSA and Air Force ran into jurisdictional uncertainty. Readers take away the founding method of intrusion investigation and the case for pursuing a small anomaly.
What the book actually covers
Stoll was not a security professional. He was an astronomer given systems administration duties, and he approached the discrepancy the way a scientist approaches an unexplained result: as something that must have a cause.
The investigation that follows is documented in almost obsessive detail, and the detail is the value. He builds monitoring to observe the intruder without alerting him. He keeps a meticulous logbook — every session, every command, every timing — which becomes the evidentiary record. He works out how the intruder is escalating privileges and moving laterally between systems. He constructs a honeypot: fabricated documents designed to hold the attacker online long enough for a trace to complete.
The institutional half is as instructive as the technical one, and considerably more frustrating. Stoll's attempts to interest the FBI, the CIA, the NSA and the Air Force in what he has found run into a wall of jurisdictional uncertainty and indifference. By Stoll's account, nobody owned the problem, because in 1986 the problem did not yet have a category. Anyone who has tried to escalate a novel risk inside a large organization will recognize every conversation.
The intruder was eventually identified as part of a group in Hannover selling access and material to Soviet intelligence.
Why it matters for your risk posture
Read it for the anomaly discipline, which is the central lesson and the most transferable one. A seventy-five-cent discrepancy was the visible edge of a state-sponsored espionage operation. The magnitude of an irregularity tells you almost nothing about the magnitude of what produced it, and the instinct to write off the small unexplained thing is the single most reliable way to miss the large one.
Read it for the investigative method, which predates the profession and holds up remarkably well. Observe without alerting the subject. Document contemporaneously and completely. Understand the intruder's objective before intervening. Preserve evidence in a form that will survive scrutiny. These remain the fundamentals.
Finally, read it for the escalation problem. Stoll's difficulty was never technical; it was getting an institution to accept ownership of a risk that did not fit an existing category. That is a permanent feature of emerging threats, and the book is an unusually honest record of what it costs.
Stoll watched the intruder before locking him out and logged every session as he went. The same sequence governs a corporate investigation into an irregularity that looks too small to matter. We preserve the evidence and establish what is happening before anyone is confronted, because an early intervention can end the visible activity while leaving its extent unknown. The record kept from the first day is what allows counsel or a court to rely on the findings later.
Key takeaways
- The size of the anomaly is not the size of the cause. Seventy-five cents led to a KGB-linked espionage operation. Investigate the unexplained, not the large.
- Observe before you intervene. Stoll's decision to watch rather than lock the intruder out is what produced the attribution.
- Contemporaneous documentation is the case. The logbook is what made the findings usable by anyone else.
- Novel risks have no institutional owner. Expect the escalation to be harder than the investigation, and plan for it.
About the author
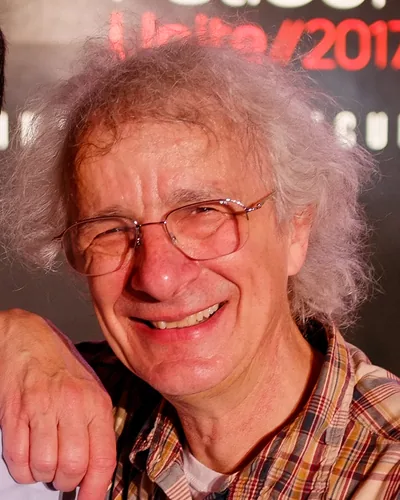
Clifford Stoll is an American astronomer who became, entirely by accident, one of the first people to conduct and document a full computer intrusion investigation. At the time he was working in systems administration at Lawrence Berkeley National Laboratory.
He wrote up the case first as a technical paper and then as this book, published in 1989. He subsequently wrote Silicon Snake Oil, a skeptical account of early internet enthusiasm, and High-Tech Heretic, on technology in education — both of which are contrarian in ways that have aged unevenly.
In the decades since, he has taught, lectured on science and made glass models of Klein bottles — mathematical surfaces with no distinct inside and outside — which is either a non sequitur or entirely in character, depending on how you read him.
Where the proceeds go
We donate 100% of what we earn to Children of Fallen Heroes
If you buy through the link above we may earn a small commission, at no extra cost to you. Every penny of it goes to Children of Fallen Heroes, a registered 501(c)(3). We keep none of it.
They are developing an 82-acre campus in Vass, North Carolina for the children of military families, first responders and foster youth — STEAM education in aviation, robotics and drones, alongside leadership and healing programs. Over eleven years their programs have reached more than 15,000 young people and families.
We participate in the Amazon Services LLC Associates Program and similar affiliate programs; these relationships do not influence our recommendations. Cookies and similar technologies record interactions with affiliate links — see our Privacy Policy to disable them, or reach us via Contact.