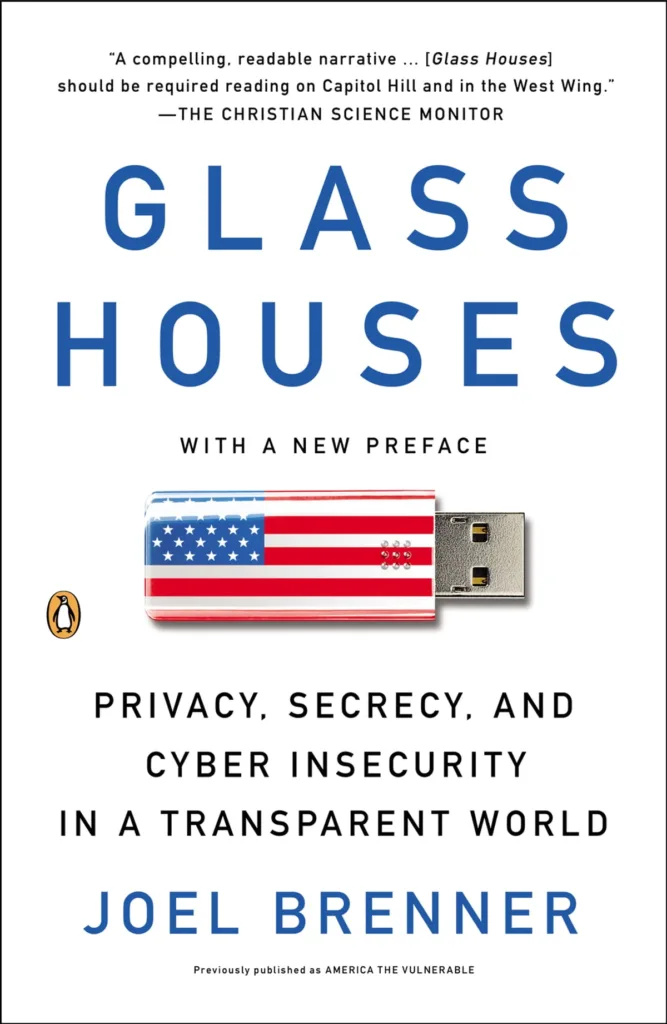
The book was published in 2011 as America the Vulnerable. The 2013 paperback carries a different title, Glass Houses: Privacy, Secrecy, and Cyber Insecurity in a Transparent World, and the same text. That is worth knowing before you order it, and it is also a small illustration of the book's own subject: the label changes, the underlying exposure does not.
Joel Brenner spent 2002 to 2006 as Inspector General of the National Security Agency and 2006 to 2009 as the National Counterintelligence Executive — the head of US counterintelligence under the Director of National Intelligence. He is therefore writing about surveillance and secrecy from inside both the agency that conducts it and the office responsible for defending against everyone else's.
His argument is that the insecurity is structural. The networks that carry commercial, governmental and personal life were built for reachability, not for confidentiality, and the openness that makes them valuable is the same property that makes them indefensible. This is not a book about better passwords.
Where it dates, it dates in the specifics — the case studies are early-2010s and some of the technology discussion has been overtaken. Where it holds up is the frame, and the frame is the reason to read it.
What the book actually covers
Brenner works through four overlapping problems: state-sponsored economic espionage, principally Chinese; the erosion of privacy by commercial data collection rather than by government; the vulnerability of industrial control systems and critical infrastructure; and the legal and institutional confusion about who is responsible for defending private networks against state-level adversaries.
The strongest chapters are on economic espionage. Brenner had visibility into the scale of intellectual-property theft from US companies and is precise about the mechanics — not dramatic intrusions but sustained, patient, low-signature collection against firms that did not consider themselves targets and had no framework for thinking about a nation-state as an adversary.
The privacy material is the most likely to surprise a reader who expects a former NSA official to argue for surveillance. Brenner is at least as concerned about what private companies assemble as about what governments collect, and he is clear that the two are connected: commercial aggregation creates a resource that states will eventually reach for.
The weakest sections are the prescriptive ones. Brenner is better at anatomizing the problem than at proposing a governance answer, and the policy chapters are noticeably thinner than the diagnostic ones. He also writes from an American institutional vantage point that a European or Asian reader will want to correct for.
Why it matters for your risk posture
Read it because it reframes the question. Most security spending is organized around controls — what we bought, what we configured, what we audit. Brenner's argument is that the exposure is a property of the architecture, and that a well-controlled organization on a fundamentally open network is still exposed. That does not make controls pointless; it makes them insufficient, which is a different budgeting conversation.
Read it for the target-selection insight. The companies Brenner describes losing the most were not the ones with the worst security. They were the ones that did not know they were interesting — mid-sized firms with a process, a formula or a customer list that mattered to someone with state resources. The relevant question is not "are we well defended" but "who would want this, and what are they prepared to spend."
And read it for the counterintelligence framing, which is rarer than it should be in commercial security. Brenner's instinct is to ask who the adversary is and what they are trying to learn, before asking what the vulnerability is. That ordering — adversary first, vulnerability second — is the habit worth taking from the book.
Key takeaways
- The exposure is architectural. Networks were built to connect, not to withhold; no control set fully undoes that.
- Not knowing you are a target is the risk. The heaviest losses fall on organizations that never modeled a state-level adversary.
- Commercial aggregation and state collection converge. Data assembled for advertising becomes an intelligence resource by default.
- Adversary before vulnerability. Ask who wants this and what they will spend, then look at your controls.
- Two titles, one book. America the Vulnerable and Glass Houses are the same text; do not buy both.
About the author
Joel Brenner was Inspector General of the National Security Agency from 2002 to 2006, responsible for the agency's internal audits and investigations, and served from 2006 to mid-2009 as the National Counterintelligence Executive, heading US counterintelligence under the Director of National Intelligence. He later returned to the NSA as Senior Counsel.
He is a lawyer by training, has practiced in private firms, and is now affiliated with MIT, where he has worked on internet policy and security. The combination — audit, counterintelligence, and law — explains the book's cast of mind: it is more interested in institutional responsibility than in technology.
Beyond the Book
- The technical case study: Countdown to Zero Day on Stuxnet, which is Brenner's industrial-control argument demonstrated in a single operation.
- The policy history: Dark Territory, thirty years of the same warnings reaching the same conclusions.
- The European view: Cyberwar, working from a different set of assumptions about industrial exposure.
- The human layer Brenner mostly leaves alone: People Hacker.
Get the book
Glass Houses: Privacy, Secrecy, and Cyber Insecurity in a Transparent World
Find it on Amazon
Where the proceeds go
We donate 100% of what we earn to Children of Fallen Heroes
If you buy through the link above we may earn a small commission, at no extra cost to you. Every penny of it goes to Children of Fallen Heroes, a registered 501(c)(3). We keep none of it.
They run an 82-acre campus for the children of military families, first responders and foster youth — STEAM education in aviation, robotics and drones, alongside leadership and healing programs. More than 15,000 young people and families have been through it in eleven years.
We participate in the Amazon Services LLC Associates Program and similar affiliate programs; these relationships do not influence our recommendations. Cookies and similar technologies record interactions with affiliate links — see our Privacy Policy to disable them, or reach us via Contact.